Repository Security Baseline
Document: INF-112Type: StandardStatus: ApprovedOwner: Cloudberrie StudioVersion: 4.2.0Updated: 2026-07-17
Current Repository Baseline
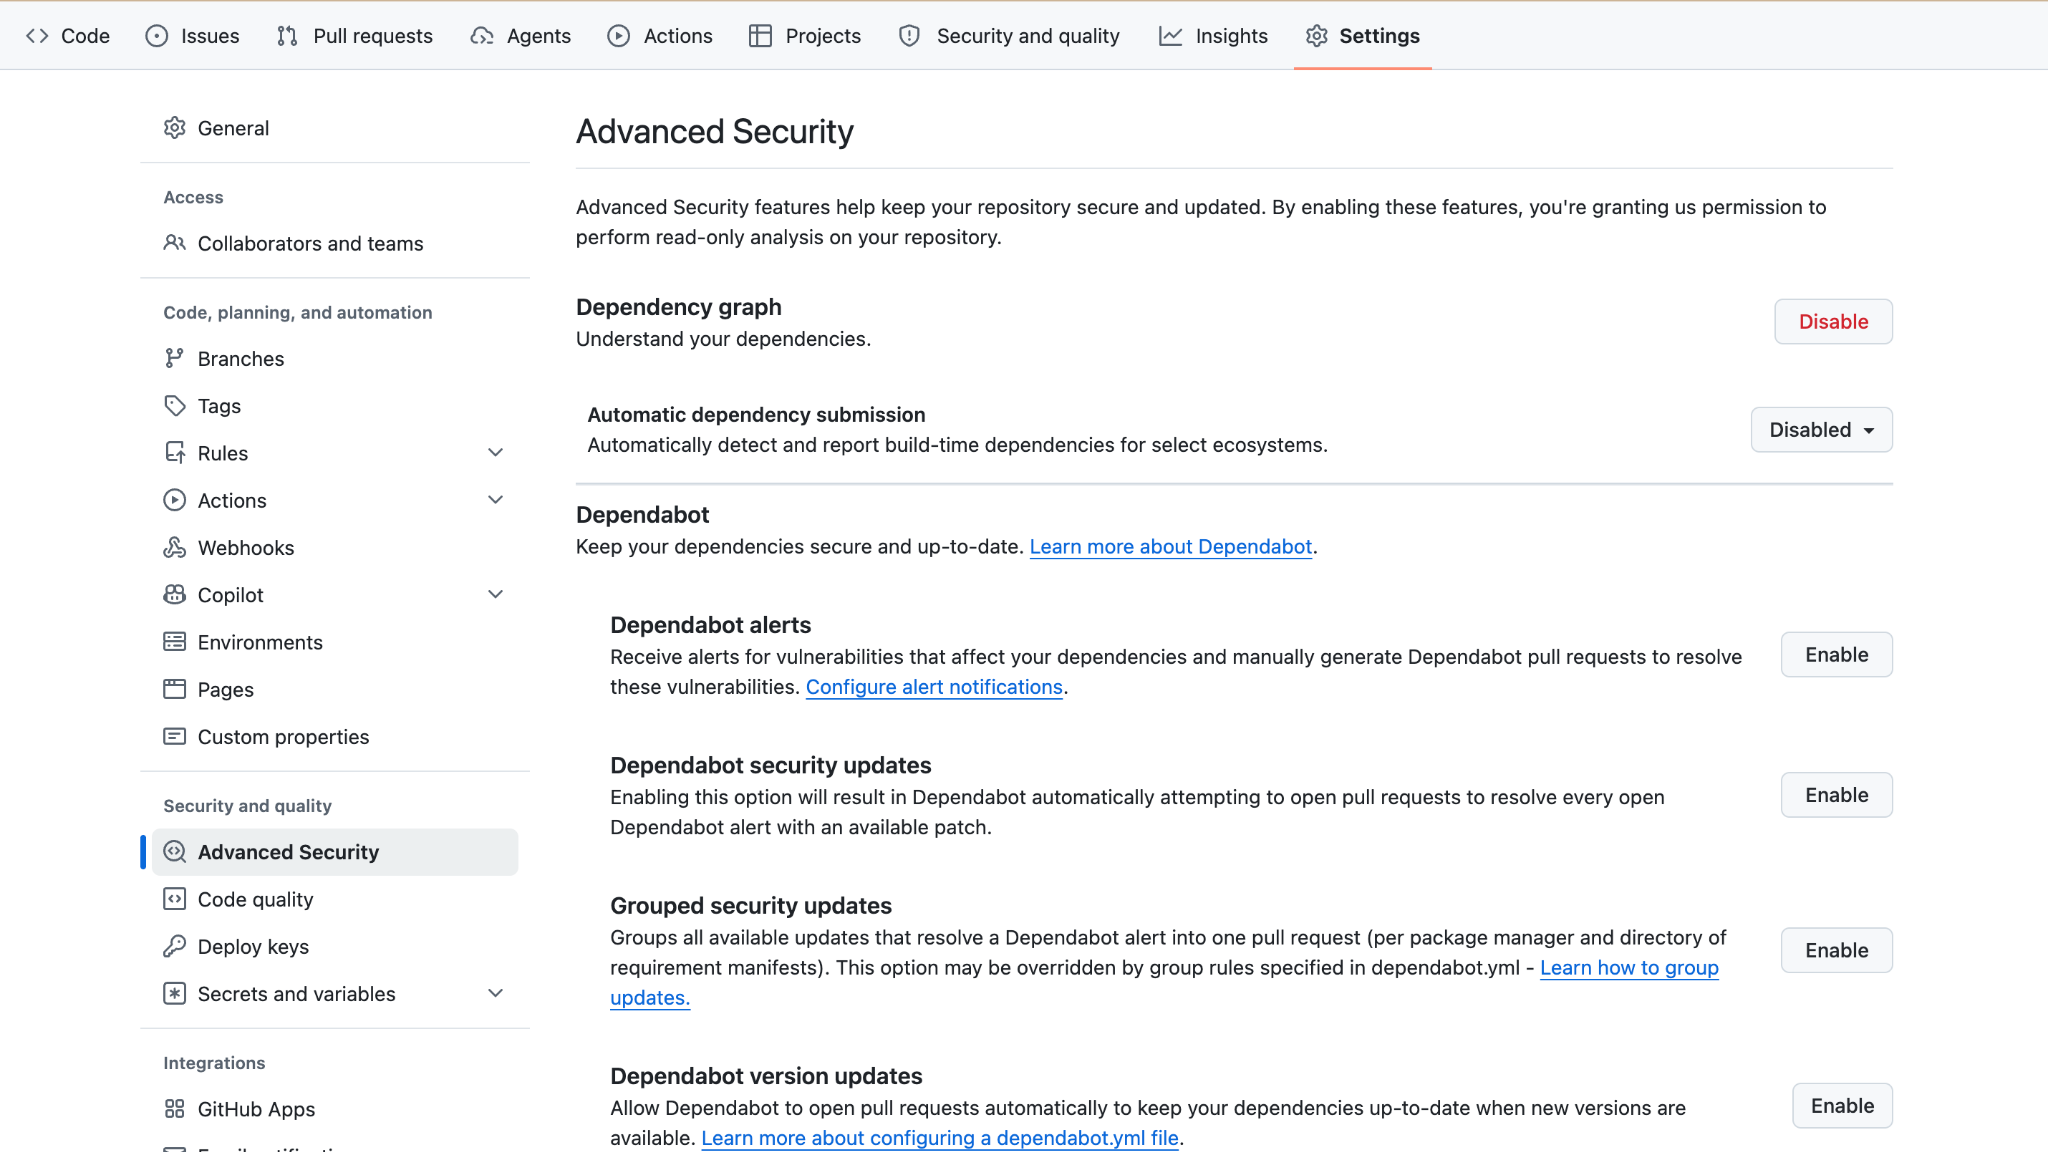
The actual cb-website private repository security options on GitHub Free.
| Feature | Cloudberrie standard | Reason |
|---|---|---|
| Dependency Graph | Enabled | Identifies dependencies and supports vulnerability alerts. |
| Automatic Dependency Submission | Disabled initially | Lock files are sufficient for the current project; revisit with advanced build workflows. |
| Dependabot Alerts | Enable | Notifies Cloudberrie about known vulnerable dependencies. |
| Dependabot Security Updates | Enable | Creates security-fix pull requests when patches are available. |
| Grouped Security Updates | Disabled initially | Keep early security changes small and easier to review. |
| Dependabot Version Updates | Disabled initially | General upgrades are reviewed intentionally to reduce breaking changes. |
| Secret scanning / Code scanning | Review when available | Visibility depends on repository type, GitHub plan, and enabled products. |
Repository Hardening Checklist
Private visibility confirmed Next.js .gitignore confirmed No open-source license Dependency Graph enabled Dependabot Alerts enabled Security Updates enabled Secrets absent from Git history Ruleset deferred or documented
Ruleset Timing
Cloudberrie intentionally defers a strict main ruleset until the first GitHub-to-Cloudflare deployment flow has been validated. After validation, introduce branch protection, pull requests, force-push blocking, and deletion protection.